Scattered oversight expectations
Vendor-risk expectations may appear across regulations, supervisory guidance, security frameworks, privacy rules and program requirements.
Monitor selected regulatory, compliance, security and guidance sources that may affect vendors, contractual obligations, questionnaires, required evidence, incident reporting and ongoing oversight. Rixena helps your team organize what changed and what may need review.
Vendor requirements can originate in sector rules, agency guidance, privacy and security obligations, contractual commitments and customer expectations. Rixena helps teams bring selected sources into one review process.
Vendor-risk expectations may appear across regulations, supervisory guidance, security frameworks, privacy rules and program requirements.
New or revised obligations may require teams to revisit standard clauses, notification terms, audit rights and contractual flow-downs.
Questionnaires, attestations and supporting evidence can change as regulators and customers refine oversight expectations.
Subcontractors, hosted services and downstream providers can affect incident response, continuity and accountability.
Select the jurisdictions, sectors and source categories relevant to your vendor ecosystem. Available coverage depends on the monitors and sources selected.
Selected regulatory and supervisory materials addressing planning, due diligence, contracting, ongoing monitoring and termination.
Developments that may affect notification clauses, audit rights, security terms, data use, recordkeeping and required flow-downs.
Changes that may influence vendor intake, risk-tiering, assessment questions, attestations and review criteria.
Selected cybersecurity, privacy, data-protection and access-control sources that may affect service providers.
Reporting, cooperation, escalation, evidence-preservation and customer-notification topics tied to third-party incidents.
Expectations related to performance review, control evidence, issue remediation, concentration risk and termination planning.
Monitor availability and applicability vary by source, jurisdiction and organization. Your team chooses the watchlist it wants Rixena to follow.
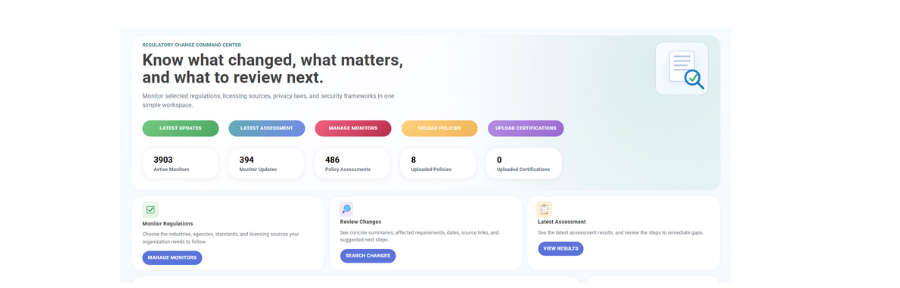
Select sources, receive organized change intelligence and optionally connect vendor-management policies for gap assessment.
Choose regulatory, supervisory, privacy, security and standards sources relevant to your vendors and services.
See source links, relevant dates, affected topics and suggested areas for third-party oversight review.
Upload and assign vendor-management, procurement, security or incident-response policies to selected monitors.
Identify areas that may need review, assign owners and organize remediation activity and supporting evidence.
Rixena follows the rule, bulletin, guidance or standard source your team selects for third-party oversight.
The update is captured and organized so reviewers can focus on vendor, contract, evidence and incident implications.
Your team receives a focused review package for compliance, procurement, security, legal and vendor-risk owners.
Rixena can support teams that oversee different vendor types, risk tiers, jurisdictions and contractual models—without forcing every third party into the same watchlist.
Create your free monitoring accountReduce repeated searches across agency, standards and sector-specific websites.
Give owners dates, source links, affected topics and review context in one place.
Connect selected changes with vendor-management and oversight policies when useful.
Organize assignments, assessments, remediation activity and supporting evidence.
Start with selected-source monitoring, then add policy assessment workflows when they support your process.
Talk to AllgressOrganizations can select from available regulatory, supervisory, privacy, cybersecurity, standards and guidance sources relevant to vendor governance. Available coverage depends on the selected monitors and sources.
Rixena can organize changes that may affect contractual obligations, due-diligence questions and evidence expectations. Your team determines applicability and decides whether templates, contracts or questionnaires require revision.
Yes. Watchlists can be organized around different services, risk tiers, jurisdictions, business units or oversight topics.
No. Policy uploads are optional. They can be assigned to selected monitors when your team wants policy gap assessment support.
No. Rixena provides regulatory intelligence and workflow support. Your organization remains responsible for determining applicability and obtaining legal or professional advice where needed.
Start a free Rixena account and build a watchlist around the vendors, obligations and sources that matter to your organization.